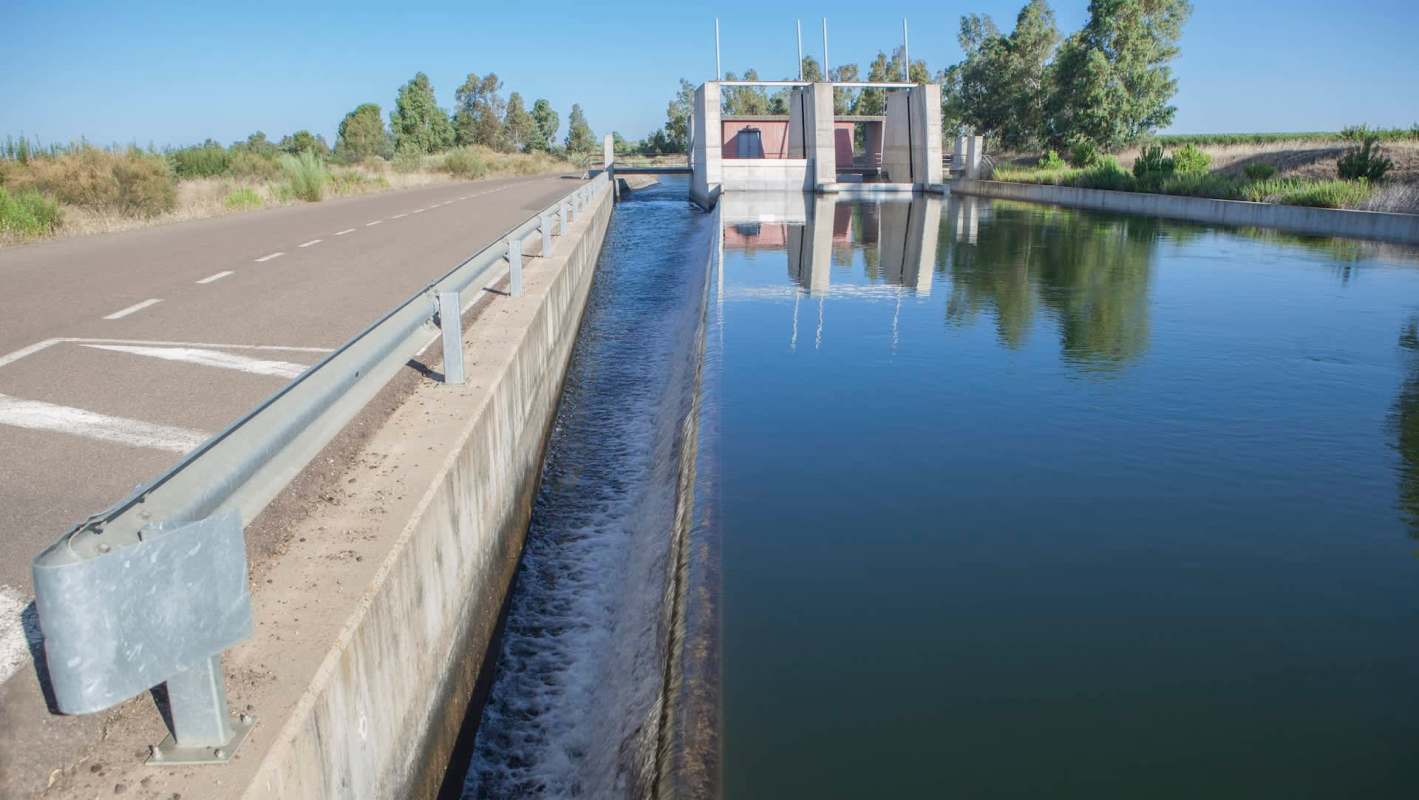
A new report from SpyCloud says malware built to harvest account data has already pulled employee credentials from almost 1,800 U.S. water and wastewater organizations.
Here's what to know
SpyCloud, the cybersecurity defense firm, analyzed roughly 10,000 organizations by reviewing more than 66,000 outward-facing systems registered with the U.S. Environmental Protection Agency, as TechCrunch detailed.
Of particular concern, SpyCloud said credentials from at least 250 organizations looked capable of reaching operational networks and remote-access tools used to run pumps and control water movement. Overall, the company found that credential-stealing malware had collected logins from 1,787 organizations, or nearly 20% of the providers in its survey.
SpyCloud separately examined an unnamed metering technology provider and found that a single infected device on its network had amassed a large volume of sensitive data, including passwords tied to 167 U.S. utility companies that used that vendor.
SpyCloud chief investigations officer Jason Lancaster said the incident effectively handed criminals the keys to "a hundred otherwise unrelated organizations" in the report.
These infostealer infections do more than expose saved passwords, TechCrunch noted. They can also take session tokens that keep users logged in, potentially allowing hackers to impersonate legitimate users and, in some cases, bypass multi-factor authentication.
TCD Picks » Quince Spotlight
💡These best-sellers from Quince deliver affordable, sustainable luxury for all

More background
These findings deepen concerns about critical infrastructure, indicating that attackers may be able to reach water-related networks without resorting to especially advanced methods.
Water systems are a particularly sensitive target because a successful cyber intrusion can affect far more than company records. These networks help manage drinking water delivery and wastewater treatment, meaning any disruption can have consequences for public health, local economies, and essential daily services.
The report arrived after a spate of water-provider breaches across the United States. TechCrunch reported the U.S. government has privately linked these breaches to Iran-backed hackers.
SpyCloud found no sign that stolen passwords drove those Iran-linked attacks. Those incidents instead appear to have involved other weaknesses, including factory-default passwords on the mechanical switches and physical controllers used by critical infrastructure.
Still, the new analysis suggests stolen credentials remain a major parallel threat. Even if a utility shuts off one point of entry, attackers may look for another, whether through poorly secured devices or employee logins already circulating among cybercriminals.
What's being done?
SpyCloud said the report doesn't show that any water utility is compromised, but it does highlight the sector's vulnerability to attack, due to its interconnected nature.
"The identity exposure sitting around this sector — a vendor's infected laptop, a stolen session, a saved remote-desktop password — is real, current, and largely invisible to the utilities it puts at risk," the report stated.
For security's sake, the firm said protecting against both identity exposure and operational technology exposure is something that the powers-that-be must do.
"Neither one is optional, and neither substitutes for the other," SpyCloud's report concluded.
Where can I learn more?
Water systems are also facing pressure far beyond cybersecurity, from invasive species to tightening standards for contaminants in drinking water.
• U.S. water managers face a call to action over invasive species spreading through raw-water transfers.
• A lawsuit against the EPA is challenging PFAS drinking water standards after a controversial court request.
• In South Carolina, experts found record levels of forever chemicals in a popular river.

Get TCD's free newsletters for easy tips, smart advice, and a chance to earn $5,000 toward home upgrades. To see more stories like this one, change your Google preferences here.