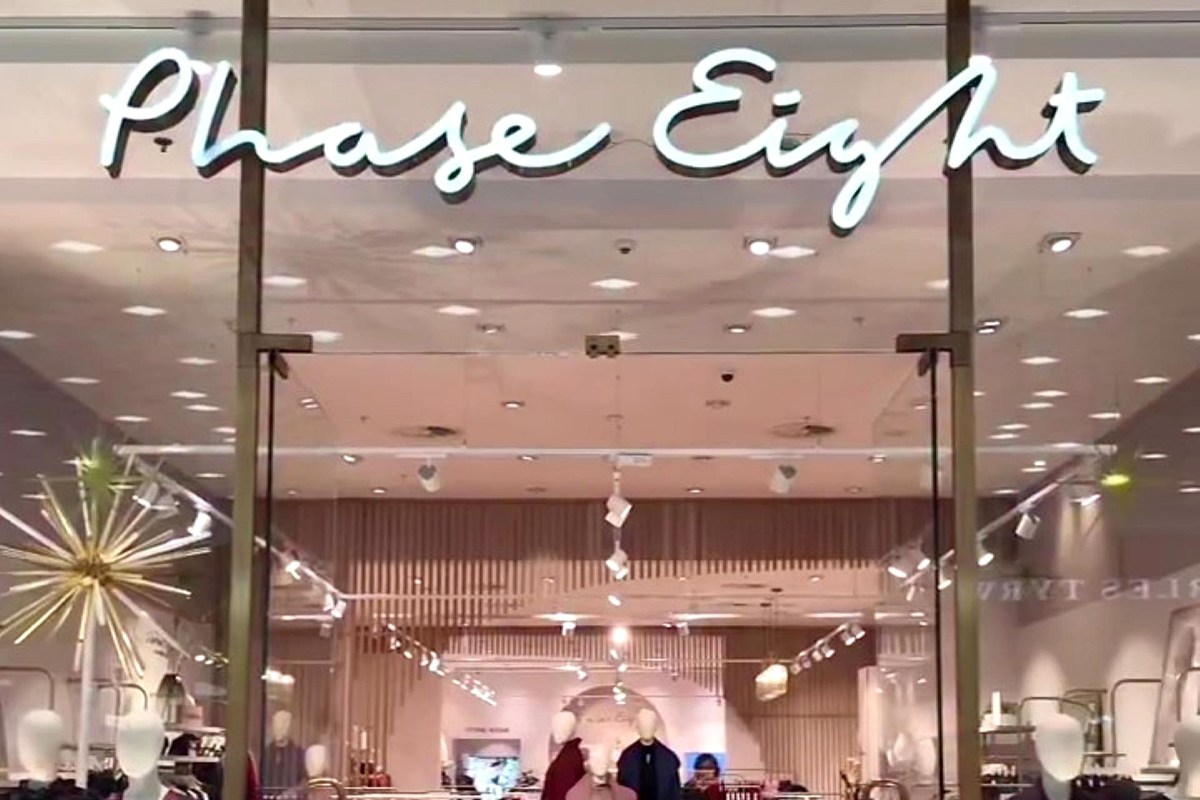
A cyber incident at the company behind Hobbs, Whistles, and Phase Eight disrupted some website functions in the U.K., adding to a growing run of retail hacks that may be exposing personal data, the BBC reported.
Here's what to know
Some online features for Phase Eight, Hobbs, and Whistles were unavailable after TFG London, the U.K. arm of The Foschini Group, identified an issue that affected parts of its IT systems.
The company added that stores were still operating as normal.
The retailer told BBC News it was "actively investigating and working with external cyber security specialists."
The disruption appears to be limited to online services, but major retailers often hold large amounts of personal data.
Charlotte Wilson, head of enterprise at cybersecurity firm Check Point, told the broadcaster that attacks targeting retailers were "starting to look rather like buses … you wait for one, and suddenly three come along at once."
TCD Picks » Quince Spotlight
💡These best-sellers from Quince deliver affordable, sustainable luxury for all

Her comments came as H&M faced a separate inquiry into a claimed attack by a notorious hacking group.
More background
According to the BBC, in an email seen by PA Media, TFG said it did not believe customers' payment information was affected.
It also indicated that it was continuing to investigate whether "any sensitive information related to our customers was impacted."
Even if card details weren't exposed, leaked personal information can cause serious problems.
Scam messages, fake account alerts, and uncertainty over whether to keep using an online account can all follow an incident like this. TFG maintained that it would contact any customers whose personal information had been affected.
Across fashion retail, cybercriminals have targeted brands from Adidas to Alexander McQueen, demanding ransom by threatening to release customer data.
"We do not believe it is necessary to change your account login information at this time," TFG's email read in part.
Even so, it can be stressful when people have to worry about online purchases potentially becoming privacy concerns when a company later discovers that stored customer information was compromised.
What's being done?
As the investigation continues, TFG is working with external cybersecurity specialists and will provide "additional updates" to customers when appropriate.
It also asserted that it would contact affected customers directly if its review found their personal data was involved.
Stores remain open while the company investigates the scope of the disruption, and some website functions may stay unavailable while the review continues.
Beverley Griffiths, senior lecturer in security and resilience at Bucks New University, told PA that customers should stay "vigilant" and watch for suspicious messages.
"No organisation is immune, so the real test of resilience is how quickly a business can detect an incident, respond and recover while keeping its customers informed," Griffiths noted.
Where can I learn more?
Other major fashion and e-commerce brands have faced other kinds of criticism from people who buy products from them.
• The EU accused AliExpress of a systemic failure to stop illegal products from reaching people shopping online.
• People shopping at AliExpress said cheap sweatpants fell short of expectations and savings.
• H&M faced criticism after people spotted tactics that encouraged overspending on low-quality fast fashion.

Get TCD's free newsletters for easy tips, smart advice, and a chance to earn $5,000 toward home upgrades. To see more stories like this one, change your Google preferences here.