A Reddit user's complaint about Claude was not just that the chatbot seemed to mistake them for a child. The follow-up concern drew even more attention: whether turning "optional data" off still means the AI reads everything a user types.
That tension among convenience, moderation, and privacy expectations quickly turned a "mildly infuriating" post into a broader debate about how chatbots actually work.
Here's what to know
The discussion started in the r/mildlyinfuriating subreddit, where the poster wrote, "Ah yes, because surely a kid has would be asking questions about college chemistry and paying bills."
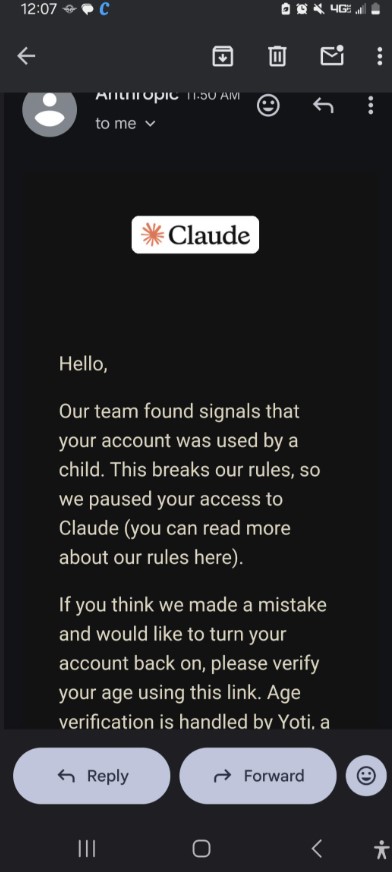
The age-related complaint was only part of what drew attention. The poster also added, "This means claude is literally looking at everything you see, even with the optional data off," shifting the focus to privacy expectations for cloud-based AI tools.
For one commenter, that concern was obvious, not surprising. They wrote, "How could any AI not be looking at everything you enter?" and followed it with, "The AI isn't isolated on your device; you enter words into it and it processes them in its data center where its programming lives. I don't see how it could do anything but that."
A different commenter focused on what happens after a system gets something wrong, writing, "They also have no support staff so you can't get it reversed, all you can do is talk to an AI bot."
TCD Picks » Quince Spotlight
💡These best-sellers from Quince deliver affordable, sustainable luxury for all

More background
The thread raised two familiar complaints about generative AI: these tools can make strange decisions about users, and people often remain unsure what privacy settings actually change.
This kind of exchange also reflects a broader infrastructure issue. AI systems are tied to the energy grid through the data centers that power them, so heavier use can mean higher electricity demand and water consumption.
At the same time, AI can help utilities forecast demand, balance renewable power, and optimize clean energy systems. The technology's role is increasingly double-edged; it may support cleaner, smarter grids while also raising security concerns, misuse risks, and pressure that can show up in household energy bills.
Some people in the thread did not see the apparent age-related response as a problem at all. One commenter wrote, "I'm glad there's at least some sort of filtering that flags the AI to potential underage users, tbh," suggesting that, for some users, imperfect moderation may still feel preferable to none.
The comments also pointed to a practical privacy issue. Even when a service offers an "optional data" setting, commenters clearly believed that did not mean prompts stayed on-device or remained unseen by the system. In this case, the concern was not only about training data but also the basic fact of remote processing.
Where can I learn more?
Concerns like those in this Reddit thread keep surfacing about how chatbots handle safety, privacy, and vulnerable users. They range from unsettling AI responses to manipulation risks and systems that ignore or misuse user input.
• A Tesla family was stunned when Grok answered a child with sexualized content.
• A college student said Google Gemini delivered a response so disturbing it lingered for days.
• Families say AI-fueled delusions spread until loved ones trusted bots over real people.
• A journalist showed ChatGPT and Google AI could be manipulated in minutes with ease.
• In London, researchers found AI chatbots ignoring user instructions more often, raising harm concerns.

Get TCD's free newsletters for easy tips, smart advice, and a chance to earn $5,000 toward home upgrades. To see more stories like this one, change your Google preferences here.