

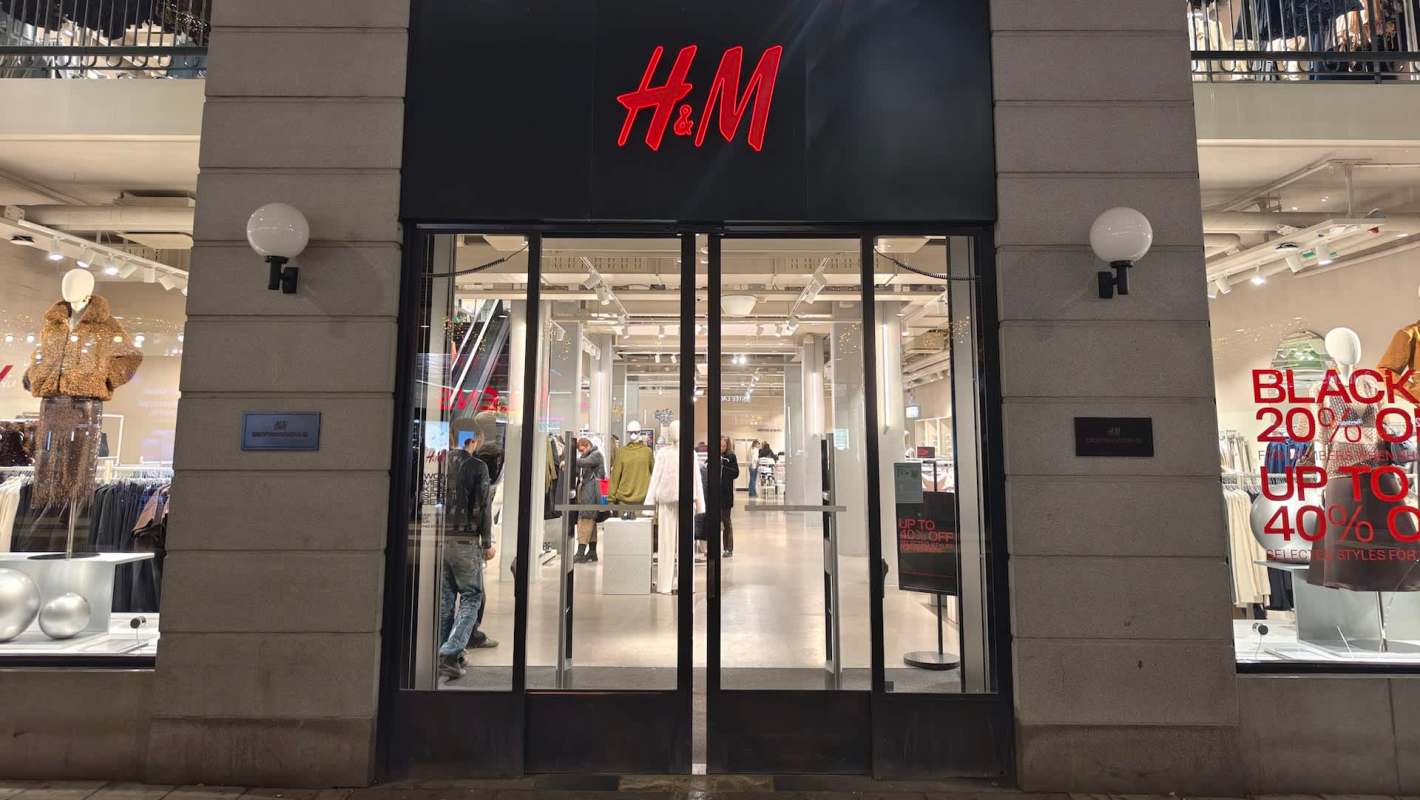
H&M Group is reviewing allegations that ShinyHunters may have targeted the retailer after ASOS announced unauthorized activity on its customer-facing platforms.
Here's what to know
The Swedish company behind H&M, Cos, Arket, and Monki said it is reviewing online reports of a possible cybersecurity issue tied to a limited amount of company data, according to TheIndustry.fashion. So far, the breach has not been confirmed.
Security researchers and past reporting have linked ShinyHunters to money-motivated cybercrime, including phishing, social engineering, and attacks that exploit weaknesses in cloud services. The group has also been associated with incidents affecting companies such as Google, Microsoft, and Ticketmaster.
The timing has drawn added attention because ASOS said on October 6 that it was looking into unauthorized activity linked to third-party systems used for customer communications. According to ASOS, the information that may have been accessed included some names, contact details, and certain account data.
ASOS said it did not believe payment card details or account passwords were involved. Even so, the case shows how retailers' choices about outside providers can shape the risks customers face when their information passes through those services.
More background
Because H&M operates thousands of stores across more than 80 markets, any data-security problem at the company affects a very large customer base. At that scale, even an unverified allegation can attract significant attention.
TCD Picks » Quince Spotlight
💡These best-sellers from Quince deliver affordable, sustainable luxury for all

For shoppers, the ASOS case is a more concrete example of the consequences people tend to worry about most. Even when payment cards and passwords aren't exposed, attackers can still use names and contact information to craft more convincing scam messages, phishing attempts, or fake account alerts.
Attackers don't necessarily need to breach a retailer's main storefront to access customer information. If employee logins are compromised or third-party services are exposed, attackers can still access data while the company's core website and app continue to function normally.
What's being done?
H&M said it is reviewing the claims and trying to determine whether they hold up. The company added that it takes potential threats to its systems and data seriously, but it has not shared more detail while the investigation continues.
ASOS said it moved quickly to cut off access to the notification platforms in question. Its response targeted the identified third-party systems rather than shutting down its retail business.
ASOS also said its website and app remained operational during the investigation. That may limit disruption for shoppers trying to place orders, but it does not erase concerns about how much customer information can sit in outsourced communications tools.
The Times reported that the U.K.'s Information Commissioner's Office had not received a report about the alleged H&M incident, meaning the situation remains at the claims-and-investigation stage.
As H&M continues its review, the company remains cautious in public. "We are currently investigating these claims to assess their validity and so far we have no indication that our data environment has been compromised," an H&M Group spokeswoman told The Times.
Where can I learn more?
Here is more coverage on separate scrutiny involving fast-fashion brands, consumer marketing, and sustainability claims.
• H&M has already faced backlash over tricking shoppers into overspending on clothes that may not last.
• In the U.K., regulators moved to investigate top fast fashion brands over alleged greenwashing claims.
• Inditex, Zara's parent company, drew criticism after a concerning operational change amid rising emissions and shipping delays.
• For online orders, experts said packaging is a more reliable sign of quality.

Get TCD's free newsletters for easy tips, smart advice, and a chance to earn $5,000 toward home upgrades. To see more stories like this one, change your Google preferences here.